Many organizations are allowing BYoD and figuring out ways to secure those devices. What are some ways I have seen this done:
- Create a VLAN and an SSID with WPA2/PSK, use ACLs to secure.
- Create VLAN(s) and use some form of MPSK/UPSK features using WPA2/PSK.
- Using WPA3 has challenges, some vendors use a downgrade method
- Some vendors are using RADIUS server.
Previously I have written up on setting up Nile – Okta SAML integration and SSO for the dashboard login. I had to setup SSO with Nile for some BYoD stuff and would like to share my configuration and setup experience. With Nile I can use WPA3 or Enhanced Open security and SSO to securely onboard devices with built in micro-segmentation.
Considering the SSO portion has already been setup, the only configuration needed is to configure an SSID. Let’s get to it.
Option 1: BYOD with Nile Guest Service
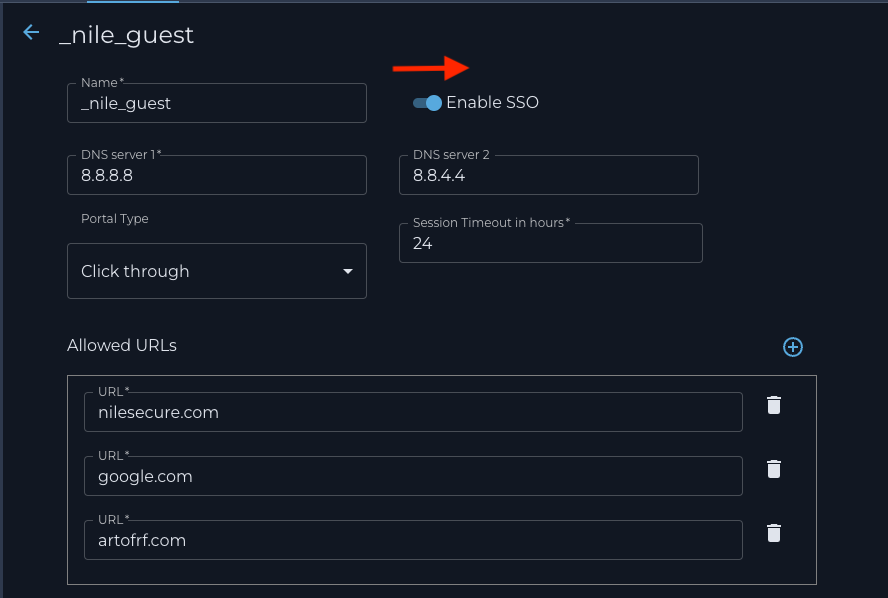
Open up Guest SSID, slide the “Enable SSO” bar to the right, click save and you are done.
Here is the connection process.
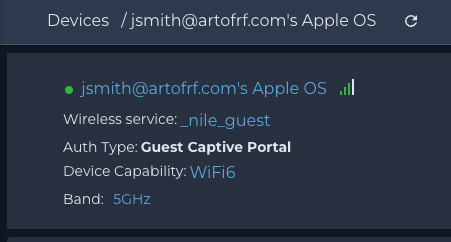
If I look at the clients in the Nile Portal now I will see the authenticated user logged in.

From the client I am able to run a quick test to see how my connection is.


I was going to pull a pcap to show the process but Nile Portal actually shows the whole connectivity process and status.
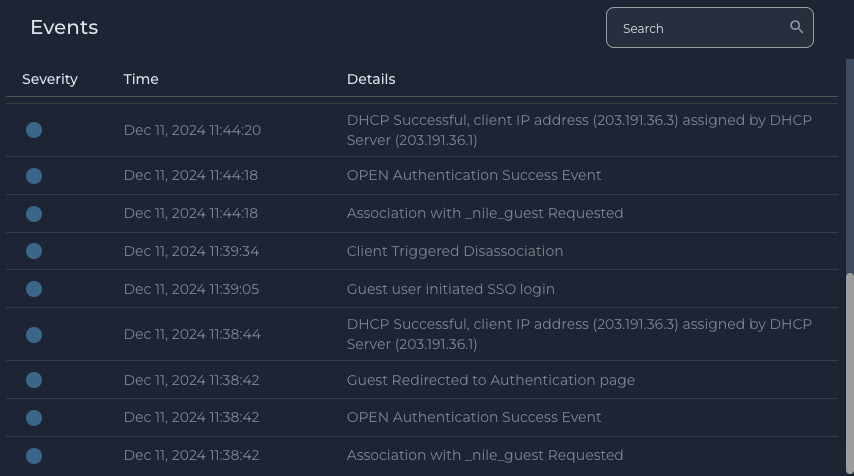

Notes: Session timeouts are for 30 days if you do not log in. But if you do at least once within the 30 days you won’t have to go through the captive portal for 365 Days unless some other event happens, for example I deleted the SSID and recreated the same SSID or changed the Click through option with email approval within the Guest SSID.
If you want the Guest SSID to use the local network, you can follow the same process under Guest SSID.
Option 2: BYOD with WPA3-Pesonal
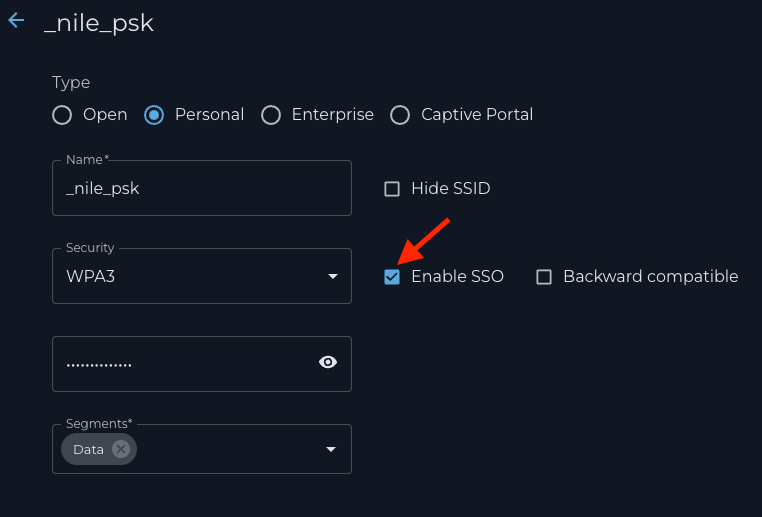
Now what if I want the BYOD to use WPA3- Personal and use one of the Segments that are part of my network. Edit the WPA3 Personal SSID and simply check the “Enable SSO” box.
Here is how the process looks like
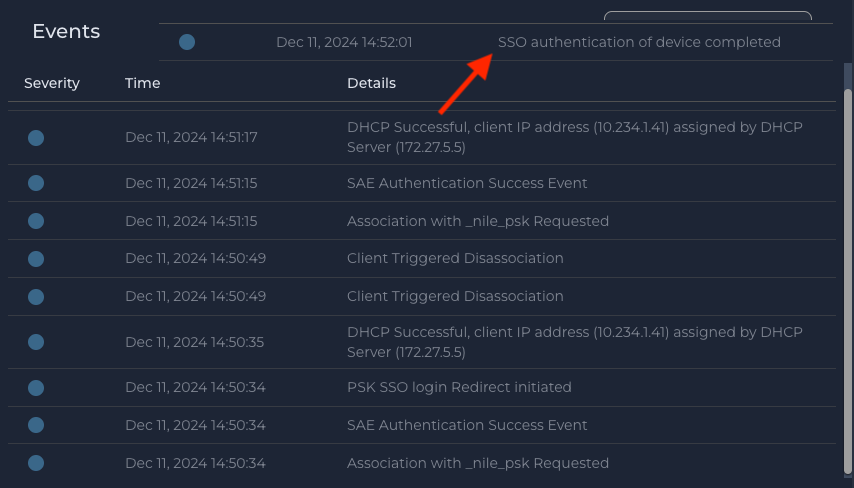
In the portal User/Device will show up with the user ID that was used for SSO login. I’m getting a private IP address this time since this traffic is terminated locally.


This is the full process shown in the Nile Portal, my local DHCP server is assigning the IP address in this scenario.
While layering SSO on top of WPA2 or WPA3 personal isn’t something I have seen, but using this method for BYOD can certainly add an additional layer of security without using any NAC solution and can provide the user information in the Nile Dashboard as well as when the clients use the “my.nilesecure.com” url to troubleshoot their device or create a ticket.
Option 3:
I am able to do this on a completely Open SSID as well. It is really this simple

Security by default:
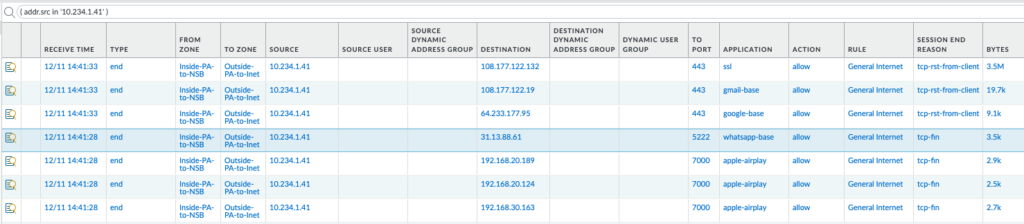
Lastly, an important factor in this solution is host based segmentation by default which is natively built into the Nile Service Block. No additional licensing, appliances, resources, complicated architecture is needed. It is there and available as soon as you turn on the Nile Service Block. Devices on the same network or across different can’t talk to each other. Giving us the choice to do what we want with that traffic. All traffic is visible in the firewall and policies can be created for that specific segment. Ability to provide secure connectivity in less than min with a few clicks makes life much easier.