
You want to use some form of network authentication, 802.1X is an option but you need a RADIUS server for it. You don’t have a RADIUS server, nor do you have any budget and resources for it.
Previously, I have written on Effortless Wi-Fi Access with SSO: Simplifying Network Authentication. Many places are starting to use more and more Wi-Fi. But there are still many places where wired devices are being used. Nile can easily extend the Network Authentication using SSO to the wired users without adding any cost and complexity.
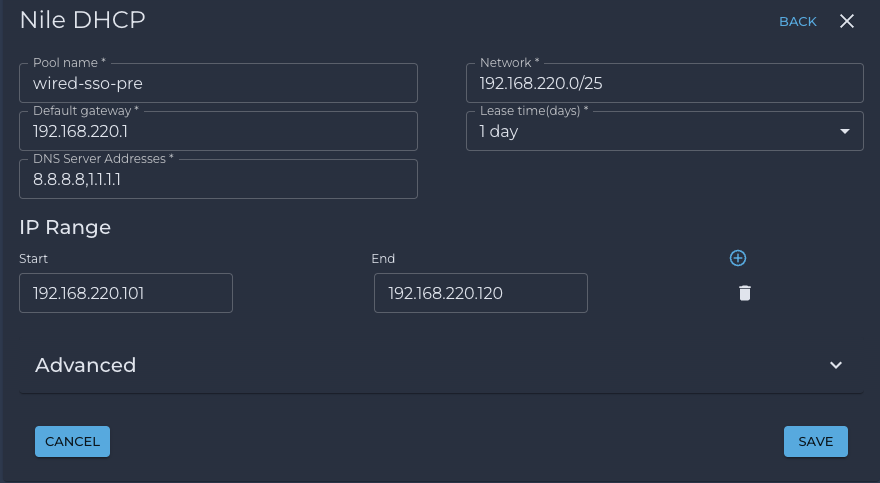
Step 1: Nile DHCP – Creating DHCP Scopes using Nile DHCP
I am going to use Nile Cloud DHCP service for this instead of using the local DHCP server. Below I created two networks in the DHCP Pool
- wired-sso-pre (For pre-auth)
- wired-sso-post (For post-auth)

Step 2: Create Segments
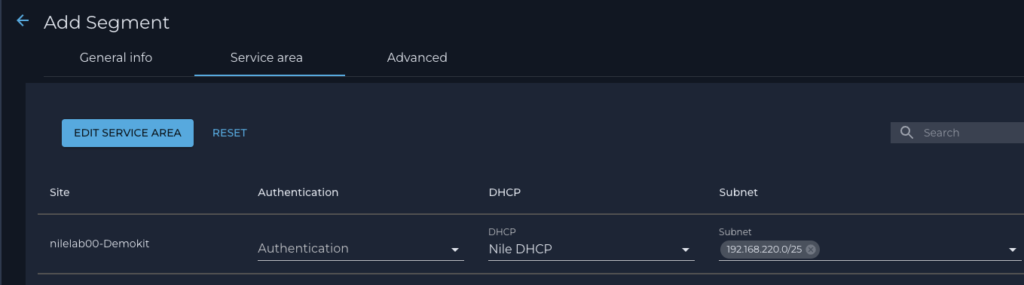
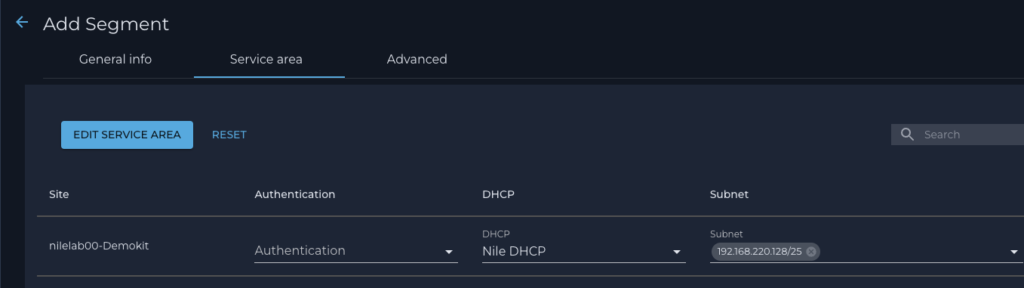
Step 3: Applying Segments
Next I applied the segments to Pre and Post Auth. NOTE: I had an “All” Rule for fingerprinting. It looks like if you have a finger printing rule setup for an OnBoarding Segment you do not get a choice to assign any “Pre-authentication segment”. The only one shows up is the one you are using for the Fingerprinting rule and that one can not be applied because it is already being used for the fingerprinting.
I had to remove the “All” Finger printing rule pointing to the OnBoarding segment to apply below.
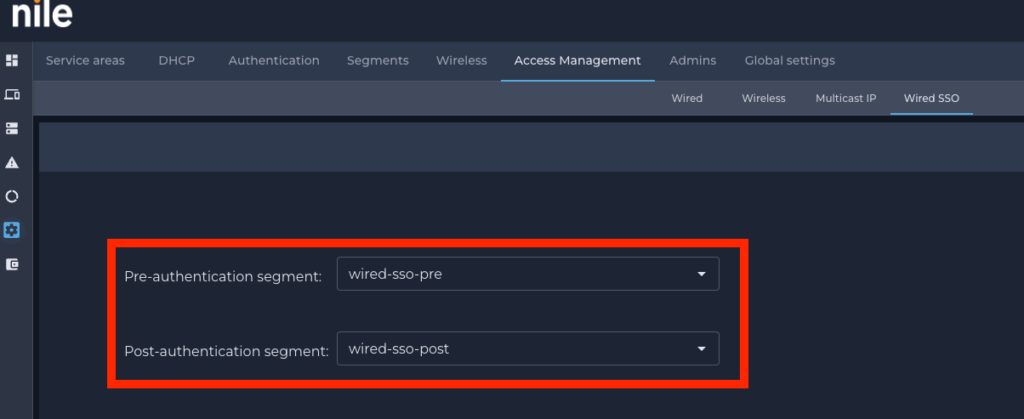
NOTE: Any devices that will not be using SSO can still end up in this “wired-sso-pre” segment. Then rules can be created to move the finger printed devices into their final segment.


Under Access Managment –> Wired now there will be a new All Rule

Note: This can also be configured under the same screen instead of first going to “Wired SSO”

Once I connect a device, it will automatically end up in the “wired-sso-pre” segment.


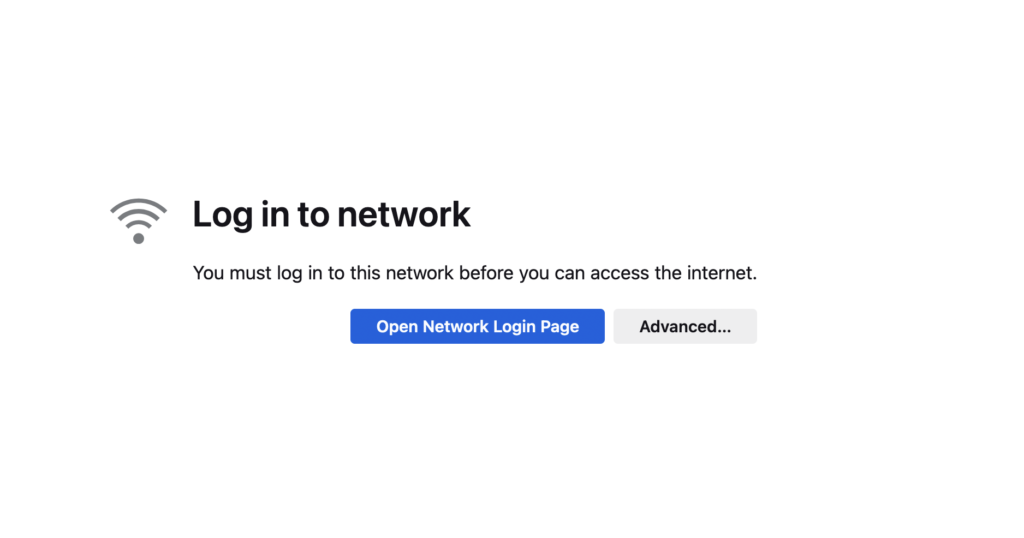
As soon as I try to open a webpage and try to browse I am redirected to this on my Mac. NOTE: Windows machines may have a different experience and I should update that later.
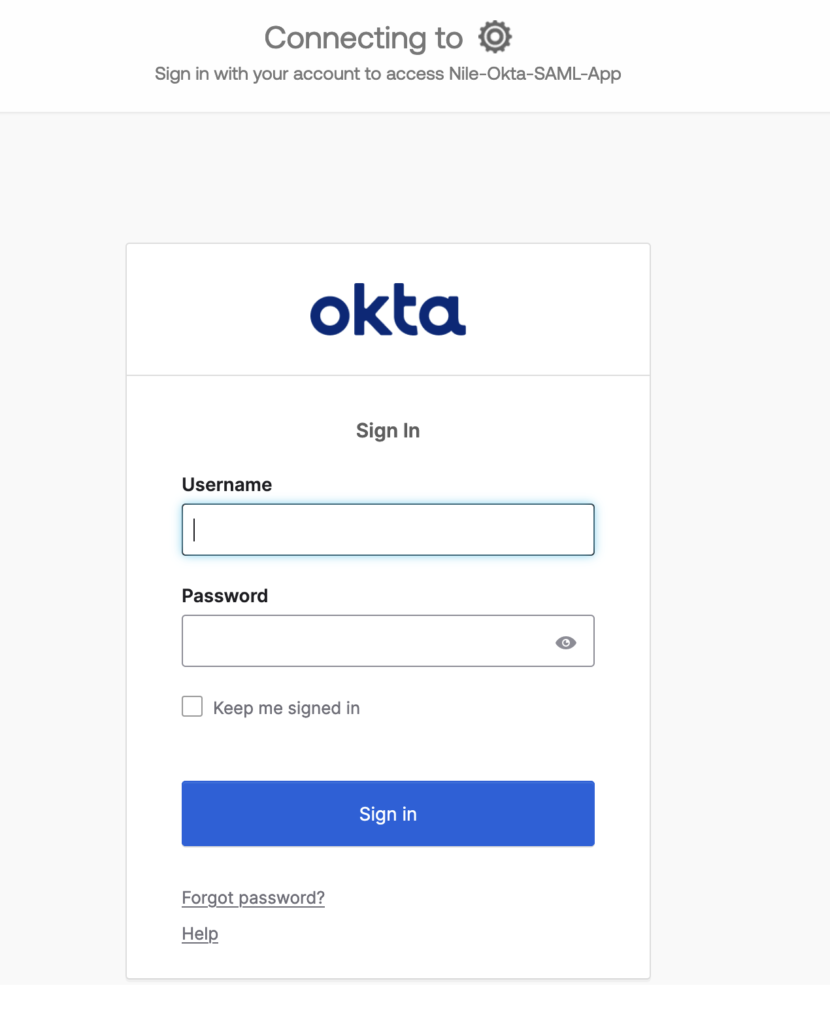
This takes me to the Okta login where I can enter my credentials.
After I complete my authentication, Nile will move my device from the “wired-sso-pre” 192.168.220.0/25 segment to “wired-sso-post” 192.168.220.128/25 segment as shown.

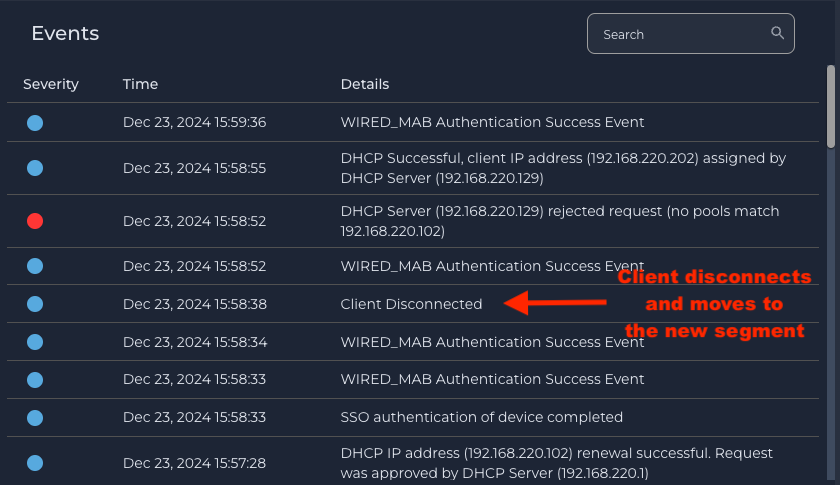
This shows the user who actually signed in as well.

Final Thoughts:
Nile providing an effortless SSO Authentication solution for wired and wireless networks provides a simple and cost effective solution for network authentication if you do not have the budget and resources to use a RADIUS server solution. You can also integrate this with SCIM as well (more on this later). Read more details and some additional information here.